What IT Support Does an Orthopedic Practice Need?
An orthopedic practice needs IT support built around imaging, surgery, and multiple locations. That means fast PACS and DICOM connectivity, an EHR that opens images without delay,...
An orthopedic practice needs IT support built around imaging, surgery, and multiple locations. That means fast PACS and DICOM connectivity, an EHR that opens images without delay,...
What Healthcare-Specialty Partnership Actually Means Healthcare-specialty experience HIPAA program leadership capability Clinical workflow understanding HITRUST or healthcare...
If your staff is already using AI, the right move is direction, not a ban. Decide which tools are approved, which are off limits, and what information can never go into any of...
What the Minimum Necessary Standard Actually Requires Purpose limitation: ePHI accessed only for stated purposes. Need limitation: only what is needed for the purpose....
A rural hospital cybersecurity plan should include seven things: a named owner and current risk analysis, multifactor authentication and account controls, email protection with...
Three Ways Clinical Security Differs From Corporate Security Time pressure: clinical staff make rapid decisions during patient hours. Security controls that delay decisions affect...
Why Risk Analysis, Risk Assessment, and Risk Management Are Not Interchangeable A healthcare CEO walking into the next executive review is rarely asked to distinguish between Risk...
To standardize IT across a multi-location medical group, start by inventorying every site, then define one standard build and roll it out in a set order: identity and logins...
The Four Things to Extract From Every HHS Settlement You Read Cited findings: which specific deficiencies HHS named Settlement amount: dollar magnitude and the factors that drove...
When a rural hospital loses internet access, it loses far more than email. Every system hosted outside the building stops: the cloud EHR, e-prescribing, lab and imaging...
Anthropic just opened its most capable vulnerability-hunting AI to far more security teams, and its early partners say it found flaws months or even years faster than they could...
Internal IT is the right choice when your company needs someone on site every day who knows your people, your equipment, and your quirks. Managed IT is the right choice when you...
Recurring computer problems put patient safety at risk by delaying lab results, interrupting medication workflows, and pushing staff into manual workarounds where patient...
The co-managed IT services that best support an overworked internal IT team take over the work that never stops or needs rare skills: 24x7 security monitoring, patch management,...
Managed IT services for healthcare work best when one accountable team owns everything between a clinician and the chart: the workstation, the login, the network, the servers, and...
To compare managed IT services for healthcare data security, look past the feature list and ask each provider to prove four things: who watches your systems after hours, whether...
Managed IT services help rural and specialty clinics with compliance by running the security controls HIPAA expects and documenting that work as it happens. Those controls include...
Growing healthcare organizations are best supported by an integrated set of managed IT services: a responsive help desk, endpoint and network management, managed security with a...
The Five Functions a Defensible Healthcare Vendor Risk Program Must Operate Tiering and inventory of all vendors handling ePHI. Due diligence proportional to vendor criticality....
What a Well-Designed Clinical Phishing Program Actually Includes Clinical-realistic scenarios Tiered intervention by impact severity Outcomes measured against actual security...
The Five Elements a Defensible HITRUST Readiness Program Requires Gap assessment substantively Remediation roadmap Evidence collection Internal validation Board governance Three...
The Five Elements a Fractional Security Executive Engagement Must Deliver Program leadership designation. Executive integration. Documented operation. Incident response...
The Six Components a Clinic Board Defense Package Must Include Regulatory obligation tied to HIPAA framework Exposure analysis with clinic-specific dollar magnitude Current...
The Six Elements of Defensible Clinical Vendor Governance Selection criteria documented. Contract review substantive. Implementation oversight. Ongoing performance review....
Where the Vendor's BAA Obligations End and the CEO's Program Begins A healthcare CEO whose organization runs on cloud, software-as-a-service, or any third-party platform handling...
Why the HIPAA Security Rule Is Being Revised — And What Changed Since 2013 The HIPAA Security Rule's last meaningful update came through the Omnibus Rule in 2013. In 2013, the...
Why a Vendor Breach Is the Hospital's Financial Problem A third-party breach involving the hospital's ePHI is the hospital's problem regardless of vendor responsibility. CFOs...
Why the CEO Should Design the Board Cyber Briefing, Not Accept What IT Prepares A hospital CEO walking into the next annual board cyber briefing is rarely framed as a governance...
Why the Tech-Operations Partnership Contract Is a Governance Instrument A healthcare CFO walking into a Tech-Operations partnership conversation is rarely framed as a contract...
Why the CEO Needs to Engage With the Risk Analysis, Not Just File It A healthcare CEO walking into the executive review is rarely asked to read the organization's HIPAA Risk...
The Six Elements a Clinical Incident Response Runbook Must Include Contact list with clinical leadership. Decision tree (clinical impact severity). Escalation including clinical...
Why the Telehealth BAA Chain Is a CFO Responsibility A clinic CFO walking into telehealth budget discussions typically sees the primary platform line. How the Telehealth Vendor...
Why Shadow IT Is an Operational Signal, Not an IT Failure A hospital or clinic COO walking into a shadow IT conversation is rarely framed as a strategic operations question. It...
The Five Risk Analysis Mistakes That Show Up in HHS Findings Incomplete scope (missing systems or vendors). Generic threat language (template rather than specific). Missing...
Where the Vendor's HIPAA Obligations End and Yours Begin A healthcare CEO whose organization runs on clinical platform vendors has signed Business Associate Agreements, almost...
What This Year's HIPAA Enforcement Record Has in Common The pattern is not subtle. HHS is not citing novel technical failures. The agency is citing the same governance and...
What Every Hospital Board Should Know Before a Ransomware Event A hospital CEO who has lived through a ransomware event has answered this question many times: *what does the board...
Why Corporate Phishing Programs Fail in Clinical Environments A healthcare COO walking into the next phishing program review typically sees click rates, training completion...
The Six-Figure Settlement Over One Unencrypted Laptop A small specialty clinic in a Midwestern state, a practice with fewer than fifteen providers, no hospital affiliation, and no...
Why "The Platform Is Compliant" Answers the Wrong Question A clinic CEO asks the IT lead whether the cloud productivity platform is HIPAA-compliant. The IT lead answers yes. The...

Why Security Investment and Insurance Work Together — Not Instead of Each Other Carrier underwriting requires the program. Coverage gaps mean residual exposure persists. HHS...

Bundled vs. Independent — What Each Model Actually Looks Like Bundled: single vendor for platform plus IT. Integration high; concentration high. Independent: separate platform...
Why Clinical IT Integration Is a Day-One M&A Decision A healthcare CEO walking into M&A integration faces a clinical IT decision under timeline pressure. The pattern is fit, not...
Direct vs. EHR-Flowed AI Vendor BAAs — What Each Architecture Produces A healthcare CFO managing AI vendor BAAs faces an architectural choice as AI footprint grows. Direct...
Why Centralized vs. Decentralized Clinical IT Is a Governance Decision A hospital system COO walking into a clinical IT operating-posture conversation is rarely framed as a...
Why the Productivity Platform Decision Needs CFO-Level Analysis A healthcare CFO walking into the productivity platform decision typically inherits a framing focused on vendor...
Why Security Operations Is a Capability Budget, Not a Tool Purchase A hospital CFO walking into the security operations decision is not buying a tool stack or a license. The CFO...
The Five Dimensions a Cloud vs. On-Prem Decision Actually Requires Capital structure: on-prem requires capital; cloud is operating expense. Operating cost trajectory: long-term...
HITRUST vs. SOC 2 — What Each Framework Actually Covers HITRUST CSF: healthcare-specific, integrates HIPAA, NIST, ISO. Higher rigor at r2 level. Expected by major healthcare...
Why Clinical IT Staffing Is a Talent Decision, Not a Procurement One A healthcare CFO walking into the IT staffing decision is rarely framed as a talent-and-risk question. It...
Your EHR going down during patient hours is not just an IT inconvenience. It delays diagnoses, pushes appointments into overtime, and erodes the trust your patients place in your...
Why the Managed IT Decision Is a Governance Choice, Not a Contract Renewal A clinic CEO walking into a managed IT decision is rarely framed as a strategic governance question. It...
The Seven Cost Components a Co-Managed IT Engagement Actually Includes Partner fees recurring. Internal staff retained. Tooling split. Training. Transition cost year one....
The Three Dimensions a Board-Defensible HIPAA Budget Requires Regulatory obligation: what HIPAA requires, what HHS expects to see, what HITRUST or accreditation requires....
Why Downtime Cost Belongs on the Hospital's Balance Sheet A hospital CFO walking into the next business continuity discussion is rarely asked to size downtime cost per hour as a...
Why the Licensing Fee Is the Smallest Part of a Clinical Platform Migration A healthcare CFO walking into a clinical platform migration typically sees the licensing and...
Why Cyber Insurance Renewal Is a Strategic Decision, Not a Procurement Task A healthcare CFO walking into the next cyber insurance renewal is rarely framed as a strategic...
What a Healthcare Fractional CISO Engagement Actually Includes A healthcare CFO walking into a fractional security executive conversation usually inherits the same framing. The...
Why the Help Desk Contract Line Misses Most of What the Clinic Actually Pays A clinic CFO walking into the help desk decision is rarely framed as a strategic cost analysis. It...
Why Breach Exposure Belongs on the Clinic's Balance Sheet A clinic CFO walking into the next budget review is rarely asked to size data breach exposure as a balance-sheet item....
Why HITRUST Is a Multi-Year Investment, Not a One-Time Budget A hospital CFO walking into a HITRUST conversation is rarely framed as a strategic certification question. It arrives...
What the Clinic CFO Is Really Being Asked at the Budget Review A clinic CFO walking into the next budget review with the IT line item flagged for scrutiny is not asking whether...
The Four Regulatory Dimensions of AI That Community Banks Need to Plan For Model risk management: explainability, validation, monitoring of AI decisions. Fair lending: AI must not...
The Four Ways Credit Union IT Differs From Community Bank IT Member-data handling: credit unions hold member data under different obligations. Cooperative service relationships:...
Nebraska IT Service Provider Celebrates a Decade of Recognition Among America’s Fastest-Growing Private Companies Five Nines Technology Group today announced that it has been...
Why MFA Is a CFO Governance Issue, Not Just an IT Control A CFO walking into MFA discussions typically inherits a framing of IT technical control. The Four Financial Dimensions of...
BCP, DR, and IR — What Each Covers and Why the Difference Matters Business Continuity Planning (BCP) addresses how the bank continues operating during major disruption. Scope:...
Why the 2023 Interagency Guidance Made Vendor Risk a CFO Governance Responsibility A community bank CFO walking into a vendor risk conversation is rarely framed as a governance...
Why the Questions the Board Asks Matter as Much as the Answers A community bank CEO walking into the next quarterly board meeting with a cyber update on the agenda has a choice....
Why "Audit-Ready" Doesn't Mean What It Did a Decade Ago A community bank CEO walking into an executive discussion about audit readiness is rarely framed as a definitional...
Why CEOs Who Understand the Exam Sequence Get Better Exam Reports A community bank CEO walking into the next FFIEC IT exam often inherits the experience secondhand. The compliance...
GLBA Safeguards in Plain Language — What a Community Bank CEO Actually Needs to Know A community bank CEO who has not read the Gramm-Leach-Bliley Act, the FTC Safeguards Rule...
What Every Community Bank CEO Should Know Before the First FFIEC IT Exam A community bank CEO who has lived through one FFIEC IT exam knows the experience. A small team of...
What a Well-Scoped Penetration Test Actually Covers Tied to Risk Assessment. Realistic scenarios. External and internal perspectives. Vendor environments and integrations....
The Six Components a Board Budget Defense Package Should Include Regulatory obligation summary tied to FFIEC framework expectations. Exposure analysis with bank-specific dollar...
The Five Elements a Cyber Oversight Committee Must Actually Operate Documented charter naming committee responsibilities. Qualified members with documented cyber training. Meeting...
The Six Elements an Incident Response Runbook Must Include Contact list (current numbers). Decision tree (severity classification). Escalation matrix. Immediate action checklist....
Healthcare organizations face a constant balancing act between accessibility, efficiency, and protection. One common question is whether cloud-hosted EHR or on-premises EHR is...
The Five Elements of an Independent Audit Report Must Include Documented scope tied to the bank's program. Methodology described substantively. Findings supported by evidence....
The Six Sections a Board Cyber Dashboard Should Actually Include Current program state in framework terms. Exposure analysis with dollar magnitude calibrated to the bank. Recent...
Why the Tech-Operations Partner Contract Is a Governance Instrument, Not a Procurement Signature A community bank CFO walking into a Tech-Operations partner renewal is rarely...
Why the Fractional Engagement Renewal Deserves Substantive CFO Scrutiny A community bank CFO walking into the fractional engagement renewal is rarely framed as a value-realization...
Cybersecurity has become as critical as capital reserves. The risks have evolved far beyond basic fraud attempts — modern attacks target your systems, data, and even trust itself....
Why the CEO Shouldn't Leave the Pen Test Report to the Compliance Team A community bank CEO walking into an executive review is rarely asked to read the bank's penetration test...
Why Vendor Risk Is Now a Finance-and-Governance Question, Not a Procurement One A community bank CFO who walks into a vendor risk conversation is rarely framed as a finance...
Why MFA Findings Are Almost Always Operational, Not Technical A community bank COO walking into MFA discussions typically inherits a framing of technical capability. MFA is...
Why Vendor Risk Gaps Land on the CFO's Books A community bank CFO walking into the next vendor risk discussion typically inherits summary reports. The Five Vendor Risk Gaps That...
The FTC Letter That Surprised a Twelve-Person Tax Firm — And What It Means for Your Business The FTC sent an inquiry letter to a small accounting practice in 2024. The firm...
In 2026, cybersecurity incidents are no longer an “IT issue”, but a boardroom-level risk. The cost of a breach goes well beyond ransom payments or system downtime — it affects...
Why the 2023 Interagency Guidance Made Vendor Risk a CFO Responsibility A community bank CFO walking into vendor risk discussions traditionally received summary reports from...
Why Ransomware Exposure Is a Balance-Sheet Question, Not Just a Security Budget A community bank CFO walking into the next budget review is rarely asked to size ransomware loss...
Why Single-Control Answers No Longer Satisfy the FFIEC Examiner A community bank CEO walking into the next FFIEC exam interview will be asked, in some form, about the bank's...
What Every Community Bank Board Should Know Before a Ransomware Event A community bank CEO who has lived through a ransomware event has answered this question many times: what...
Why the Same Findings Keep Appearing Every Exam Cycle A community bank CEO walking into the next FFIEC IT exam often sees a familiar list of likely findings. The bank's compliance...
For many businesses, cybersecurity can still feel like a “someday” investment — something to prioritize once the next project launches or budgets open up. But the reality is that...
What This Year's Exam Findings Have in Common The pattern is not subtle. The regulators are not citing novel technical failures. They are citing the same governance gaps...
The Five Dimensions a Cloud Decision Actually Requires Data residency and sovereignty: where data lives, regulator implications. Audit logging capability: meets FFIEC monitoring...
The Banks a Single-Specialist Model Actually Fits Banks with limited internal capacity to manage multiple vendor relationships, banks where integration value is high, and banks...
Why Exam Preparation Model Is a Discipline Question, Not a Sourcing Question A community bank COO walking into the next exam preparation cycle has a choice. The pattern that...
Why Compliance Documentation Is a Function Design, Not a Procurement Decision A community bank COO walking into the compliance function design discussion is rarely framed as an...
Why the Centralized vs. Decentralized Decision Shouldn't Be Made by Default A multi-branch bank's COO walking into an IT operating-posture conversation is rarely framed as a...
Why the Bundled vs. Independent Decision Belongs at the CEO Level A community bank CEO walking into the bundled-vs-independent decision typically inherits a framing of operational...
Fractional vs. Full-Time: What the Decision Is Actually Choosing Between A community bank CFO walking into the security executive decision is not choosing between two equivalent...
Cybersecurity isn’t just an IT issue anymore — it’s a business issue. Every year, cyber threats evolve in sophistication and scale, targeting organizations of all sizes and across...
Why the "Just Insure It" Argument Keeps Coming Back A community bank CFO walking into a cyber budget review will eventually hear the substitution argument. It comes from...
Artificial intelligence (AI) is no longer a buzzword floating around tech conferences — it’s a real, powerful force shaping how we work, communicate, and make decisions. Whether...
The Security Operations Decision Belongs in the CFO's Office A community bank CFO walking into a security operations decision is rarely framed as a strategic question. It arrives...
Why the IT Operating-Model Decision Is a Governance Choice, Not a Renewal A community bank CEO walking into an IT operating-model conversation is rarely framed as a strategic...
Why the Year-One Price Comparison Misses Most of the Cost A community bank CFO walking into a co-managed IT decision typically sees the partner proposal price first and the...
Why the Cyber Budget Is a Governance Question, not a Line Item A community bank CFO walking into the annual board budget review with the cyber and IT line item is rarely framed as...
Why Branch IT Refresh Is a Capital Planning Problem, Not a Project Budget A community bank CFO walking into the branch IT refresh discussion is rarely framed as a multi-year...
Why the Total Cost of a Finding Rarely Shows Up on One Line A community bank CFO walking into the post-exam discussion is rarely framed as a strategic cost analysis. It arrives as...
Reactive IT waits for things to break; preventative IT works to stop them from breaking in the first place. For a growing, regulated business, that difference has a major impact...
Why the Annual DR Test Is an Operations Question, Not a Calendar Item A community bank COO walking into the next disaster recovery test is rarely framed as a strategic operations...
What Security Operations Is Actually Buying You A community bank CFO walking into the security operations cost discussion is not buying a tool stack or a license. The CFO is...
Why Cyber Insurance Is a CFO Problem, Not a Procurement Task A community bank CFO walking into the next cyber insurance renewal is rarely framed as a strategic risk-transfer...
If it feels like your EHR system freezes the moment your waiting room fills up, you are not imagining things. IT downtime seems to strike during patient hours because that’s when...
What "In-House IT" Actually Means at a Community Bank A community bank CFO walking into a budget review with the IT line item flagged for scrutiny is rarely looking at the full...
What "Fractional CISO" Actually Means at a Community Bank A community bank CFO walking into a fractional security executive conversation usually inherits the same framing. The...
Business “growing pains” are a good problem to have — but it’s a bigger problem if your IT environment is not ready for your growth. What worked when you had 20 employees, one...
Framing the Real Cost Question The community bank CFO who walks into an annual budget review with the cyber line item flagged for scrutiny is not asking whether the bank can...
Hiring more IT staff sounds like a straightforward way to solve technology problems — but it is not always the most effective or efficient path. In many cases, the real issue is...
As businesses grow, so do their technology needs — and one of the biggest questions they face is how to manage IT. Should you build a robust internal IT team, or partner with an...
HIPAA compliance is not just about policies and paperwork. It lives and dies in the day-to-day reality of how your systems store, transmit, and protect patient data. Even if your...
Building an internal IT team sounds like the natural next step toward a growing business. You hire a few smart people, give them the right tools, and expect technology to run...
In healthcare, technology should be an asset — not an obstacle. But as your organization grows, the legacy structures that once supported your daily workflows can start to slow...
Most organizations have a line item for “IT”. Hardware, software subscriptions, maybe an IT operations partner or internal staff… yes. But some of the most expensive technology...
Organizations rarely fire their IT provider after one incident. It usually comes after months of mounting frustration — a long stretch of slow responses, recurring problems, and...
Managed IT isn't one-size-fits-all. Different pricing models serve different needs, and not all deliver the same value — especially for regulated industries like healthcare and...
For many organizations, the idea of partnering with an IT provider raises an immediate concern: Will this replace my people? After all, your team knows your business inside and...
Technology invisibly powers nearly every interaction your customers have with your business — from the moment they visit your website to the second they receive a service update...
When you partner with a managed service provider (MSP), the goal is simple: get IT off your plate so you can focus on running and growing your business. Over time, you should feel...
Technology shouldn’t hold your business back; it should give you the confidence and stability to move forward. But for many growing organizations, IT support starts as a...
In today’s business landscape, technology isn’t just a behind-the-scenes necessity — it’s the foundation that enables growth, agility, and confidence. Yet many organizations...
Technology is the backbone of every modern business, but how you manage it makes all the difference. Many organizations today work with a Managed Service Provider (MSP), a company...
How many times have you seen cybersecurity breaches in the news in the last year? If you can recall even one time, we think that is one too many. Why? Because that one news story...
You might be thinking to yourself, cyber insurance… is it really necessary? Think about it this way - Cybercrime Magazine predicts that ransomware costs will reach $74 billion...
Surfing the web plays such a strong role in the daily lives of users, that it's almost uncomfortable to imagine life before it. As technology has advanced, so have its users,...
While you hear about the occasional breach of Protected Health Information (PHI) from large organizations, smaller medical offices often believe they are safe from a breach due to...
Small to medium-sized businesses are consistently targets of cyber-attacks due to their size and underestimated security measures. According to the ITRC 2025 had a record total of...
Great communication starts with the right tools. Unified Communication as a Service (UcaaS) is not a new concept nor is it a niche market, its market size was valued at USD $66.42...
In the IT industry, we IT folks often assume that users understand all the language and processes. Which is why when the topic of Managed IT Services is discussed, we assume you...
In recent years, billions of people have been affected by various data breaches and cyberattacks. Not only have these victims lost money or valuable data, but they also lost their...
In the tech industry today, even the most reliable tools can be used against you. Five Nines has recently discovered phishing attempts that are in the form of an Office 365...
To put it simply, risk can cost you… and it can cost you a lot. Unfortunately, risk will always be a factor when it comes to business technology. How you choose to eliminate...
In today's world, technology is on-the-go... and there are no trends to show that this on-the-go tech culture will be slowing down. Neat. states in 2025, over 32.6 million...
There's a reality where your IT operations can break out of the endless break-fix cycle. The most common challenge for IT Directors in mid-sized organizations is balance – there's...
Organizations with limited IT staff and resources face growing pressure to manage both day-to-day technical operations and strategic, business-specific IT initiatives....
At Five Nines, we understand the unique challenges rural hospitals face because we've seen them firsthand. With experience supporting more than 85 healthcare organizations and 15...
SMS phishing (“smishing”) is a form of phishing in which an attacker uses SMS text messages to trick recipients into taking an action and compromising sensitive information....
The 2020 onset of the COVID-19 pandemic resulted in a rapid increase of remote working, and the years that followed created a culture of hybrid work, a boom in smaller satellite...
As cloud computing solutions flood the business world, one question comes up frequently for businesses hosting on-premise solutions: “Should we move (even part of) our data center...
Azure Virtual Desktop (AVD) is a set of technologies from Microsoft Azure allowing IT professionals to create virtual desktops and remote apps in Azure and publish them to users...
Support for Microsoft Windows 10 ends October 14, 2025. After this date, Microsoft will no longer provide free security updates, patches, or any technical support for machines...
We've seen the statistics, we've heard the horror stories, and we understand. The reality behind how often customer experiences go wrong or problems go unsolved is alarming, and...
Do you patch all critical vulnerabilities within 'X' days? If you've dealt with an audit, cyber insurance, or third-party vendor due diligence, you've probably seen some variant...
Typing in a simple username and password is no longer enough to protect your data in the business technology world, which is why multi-factor authentication is such an important...
What's your go-to password? We all have one. Is yours secure? You can test how secure one of your top-of-mind passwords really is by checking it here:...
We'd like to throw a quick statistic your way. According to Verizon's Data Breach Investigations Report, over 74% of all breaches include a human element in some way. Why is this...
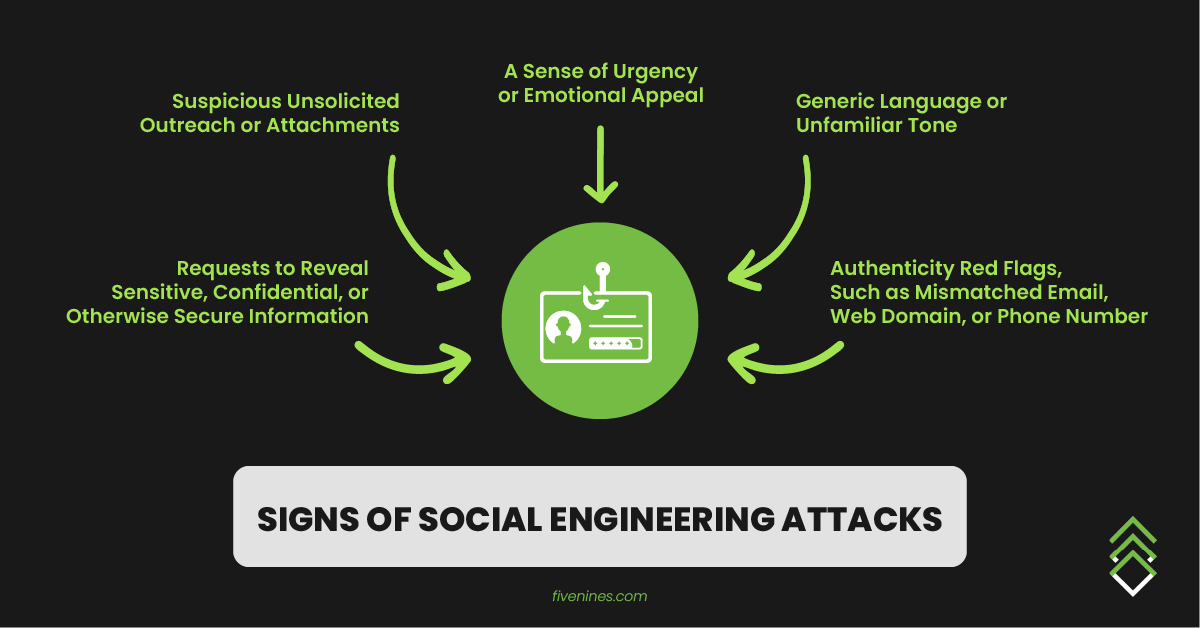
It's true – your devices, accounts, and data are all incredibly valuable to cyber criminals, no matter your industry or role. According to Verizon’s 2024 Data Breach Report, 68%...
The AT&T phone record breach – which took place in 2022 and was disclosed July 2024 – affects everyone. Even if you're not an AT&T customer, records of calls placed and text...
Microsoft 365 Copilot is an AI-powered assistant that is built into the Microsoft 365 suite of applications including Word, Excel, PowerPoint, Outlook, and Teams to provide...
Information released from the Change Healthcare ransomware attack in February 2024 reveals the absence of Multi-Factor Authentication on a remote-access tool that attackers used...
Unified Communications is an important business component meant to optimize processes and increase user productivity. It is something that relies on successful technology in order...
It's a harsh reality for most small and mid-sized businesses, but it's the truth. You simply don’t have the resources to stop well-funded, highly-targeted attacks. But that's not...
Have you had an issue with email deliverability or your domain being flagged as spam? The industry standard for spam complaints is 0.1%. This means if you send an email campaign...
In a recent development, both Yahoo and Google have chosen to make DMARC a requirement for email delivery. This move is a significant step toward enhancing email security and...
Your team spends time and money on your IT resources, so it's only fair to make sure they are being utilized to their full potential. It's important that IT experts ask the right...
The new year is quickly approaching. That's right, it’s already time to start strategically planning to hit next year’s IT goals. Our rule of advice is that your team should sit...
Discover which IT service model is right for your medium-sized business. What are Co-Managed IT Services? Co-managed IT services can be a game-changer for medium-sized businesses...
"When was the last time you restarted your computer?" Does that question sound familiar? Whenever a user is facing a tech issue, typically one of the first troubleshooting steps...
The world of technology is always changing. Recently, IT has become a multifaceted Human Resource issue as companies look to hire good IT people, find someone with the knowledge...
There are only a few times throughout the year when it is encouraged to "unplug" from your work, when you should spend time with family, eat too much food, and turn your attention...
AI, with its immense potential, is reshaping the realm of cybersecurity. The integration of AI into the already overwhelming list of today’s cyber threats can seem daunting. It’s...
As another year flies past, is your technology accounted for? In order to keep a well-maintained IT environment, you must make your technology a part of your annual strategic...
The Microsoft Endpoint Configuration Manager (MECM), formerly known as System Center Configuration Manager (SCCM), is a Microsoft systems manager that allows administrators to...
Microsoft Azure is a growing collection of more than 200 integrated cloud-based products and cloud services spanning analytics, computing, database, networking, storage, and more....
If you’re looking for the best solution for a hybrid work environment, look no further than the Microsoft Teams Platform – built for communication, collaboration, and...
To view the recording of our Tuesday Tech Talk, click HERE. Over the last 12-15 months, staffing conversations have taken a turn that not many people expected, especially staffing...
To view the recording of our Tuesday Tech Talk, click HERE. Cybersecurity incidents continue to make the news. Here is the Five Nines’ take on typical breaches and how to avoid...
Microsoft's suite of business productivity products is constantly evolving – both in name and in technical capabilities – so it can be challenging to keep track of what's what if...
No matter the industry, cybersecurity will be critical to your organization’s long-term success. In our first Tuesday Tech Talk of the year, Jarrod Daake, our Director of...
Strategic IT Planning is a collaborative process taken with clients to understand their business needs and goals, that ultimately allows the IT budget to appropriately align with...
Website breaches can cost millions of dollars and thousands of hours to remediate. Joe Brown, Five Nines Director of Marketing Operations, knows firsthand. In his career, he has...
We partnered with HBE CPAs & Consultants to present Security Tips to Keep You Safe at Home & Work, and here are the top 5 tips we covered: #1 – Practice Good Password Hygiene To...
You come to work with all systems operational: patients are being checked in. Nurses are filling out charts. Doctors are prescribing medicine. Everything in your hospital is...
We’ve talked a lot about the importance of changing your password and making sure you choose passwords that aren’t easily guessed. But while you should always beef up your...
It’s likely your company depends on several pieces of technology to consistently deliver a seamless product or service to your customers. When you consider that, protecting your...
Cloud services have modernized the way company's work and allow for collaboration in any place, with any device. At Five Nines, we’re big fans of Office 365 applications, but...
As technology continues to change, the number of ways your company can be targeted in a malware attack grows. At Five Nines, we put a major emphasis on educating our clients about...
It's likely you have insurance plans for all of the unforeseen circumstances in life: apartment fires, cell phone accidents and even getting sick. You may think of these plans as...
As business owners, we typically prefer not to think about what would happen if we suddenly lost all of our company’s data and crucial information through a breach or accident....
It’s all too easy to forget how integral and pervasive software-as-a-service (SaaS) has become to modern business operations, given the efficiencies and flexibility benefits it...
Change is hard. Ask any business owner and they’ll tell you that the slightest change can cause ripple effects throughout an organization if not properly administered. Changing...
As a leader in your company, you’ve done the research and know that moving toward a managed IT services provider is what is best for the success of your business. The concern?...
After the public and finance sectors, the manufacturing industry is the third most targeted by cyber-attacks, as the threat from malicious hackers, cybercriminals and corporate...
When it comes to working with your team, collaborating with another company, or simply working on a project from multiple locations, everyone wants to network and feel connected...
Cybercrime is a real threat to all businesses, SMB's included. Statistics are only showing an increase in cyberattack methods, and successful attacks result in a significant loss...
Solve. Secure. Advance. You have seen these 3 words beneath our logo since our rebranding back in 2015. This phrase is incorporated in everything we do: it drives the way we...
In all aspects of business, there is typically some form of documentation. You could be tracking certain numbers for goal completion, documenting budgets, or analyzing metrics for...
